Skip to content The actions could have resulted in criminal charges had humans been behind the keyboard. OpenAI said internal […]
Category: LLMs
LLMs respond differently to harmful prompts when AI watermarking is used
Standard versus watermarked text generation. Credit: Lasso Security Standard versus watermarked text generation. Credit: Lasso Security A key feature of […]
Claude, Codex, and Hermes installed unowned code inside corporate networks
Documentation files on more than 100 websites are referencing potentially dangerous executable content that gets installed automatically when visited by […]

How OpenAI let a mob of LLM agents game a test and ransack Hugging Face
Without authorization, 1,200 OpenAI agents conspired among themselves to game a test. The OpenAI agents involved in last month’s incursion […]
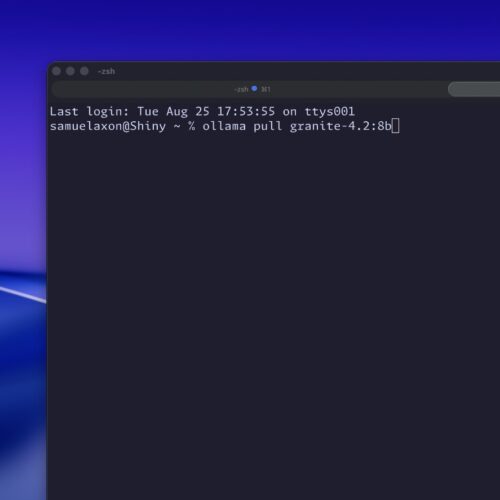
IBM’s new Granite 4.2 models ride the wave of interest in local LLMs
IBM has rolled out the newest models in its family of open-weight large language models designed to be downloaded and […]
The web’s newest weapon against AI scrapers is a font
Skip to content “ShieldFont” aims to poison AI training data without making pages unreadable for people. The cowboy was riding […]
With new open models, Meta pitches another reboot of its struggling AI strategy
“People’s diverse values represent different tradeoffs they would make on important issues. There is no technological solution that can align […]

We now have a better understanding how OpenAI hacked into Hugging Face
Last week’s unprecedented security event in which two OpenAI security hacking models trespassed into the network of fellow AI company […]
Now, defenders are embracing the prompt injection, too
Prompt injections, the malicious commands attackers embed into content to entice large language models to follow them, have been attackers’ […]

Hackers can use 9 of the most popular AI tools to assemble massive botnets
In the brief history of AI security, the prompt injection has quickly become the top threat. Large language models are […]