Ravie LakshmananOct 09, 2026Vulnerability / Network Security

Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service (DoS) under certain conditions.
“CVE-2026-107406 is a memory overflow vulnerability that may lead to remote code execution or denial-of-service under specific configuration conditions,” Citrix said.
The vulnerability carries a CVSS score of 9.5 out of 10.0. There is no evidence that the issue has been exploited in the wild. Citrix has credited Michael Tucker, Chew Keong Tan, and Alex Bernier of the JPMorgan Chase XOR Team, along with Maxim Suhanov, for discovering and reporting the flaw.
Successful exploitation hinges on the NetScaler deployments being configured as a SAML identity provider (IdP) or service provider (SP). Customers can determine if their instances meet the criteria by checking the configuration for entries like below –
- SAML SP: add authentication samlAction
- SAML IdP: add authentication samlIdPProfile
The issue impacts the following versions –
- When configured as a SAML IdP –
- NetScaler ADC and NetScaler Gateway between 14.1-73.37 and 14.1-73.41, inclusive
- NetScaler ADC 14.1-FIPS between 14.1-73.37 FIPS and 14.1-73.41 FIPS, inclusive
- NetScaler ADC and NetScaler Gateway between 13.1-64.23 and 13.1-64.28, inclusive
- NetScaler ADC 13.1-FIPS between 13.1-NDcPP 13.1-37.279 and 13.1- 37.282, inclusive
- When configured as a SAML SP or SAML IdP:
- NetScaler ADC and NetScaler Gateway before 14.1-73.37
- NetScaler ADC 14.1-FIPS before 14.1-73.37 FIPS
- NetScaler ADC and NetScaler Gateway before 13.1-64.23
- NetScaler ADC 13.1-FIPS before 13.1-NDcPP 13.1-37.279
“Secure Private Access Hybrid deployments using NetScaler instances are also affected by the vulnerability,” Citrix warned. “Customers need to upgrade these NetScaler instances to the recommended NetScaler versions to address the vulnerability.”
The shortcoming has been addressed in the versions below –
- Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1-73.46 and later releases
- Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1-64.29 and later releases of 13.1
- Citrix NetScaler ADC 14.1-FIPS 14.1-73.46 FIPS and later releases of 14.1-FIPS
- Citrix NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.283 and later releases of 13.1-FIPS and 13.1-NDcPP
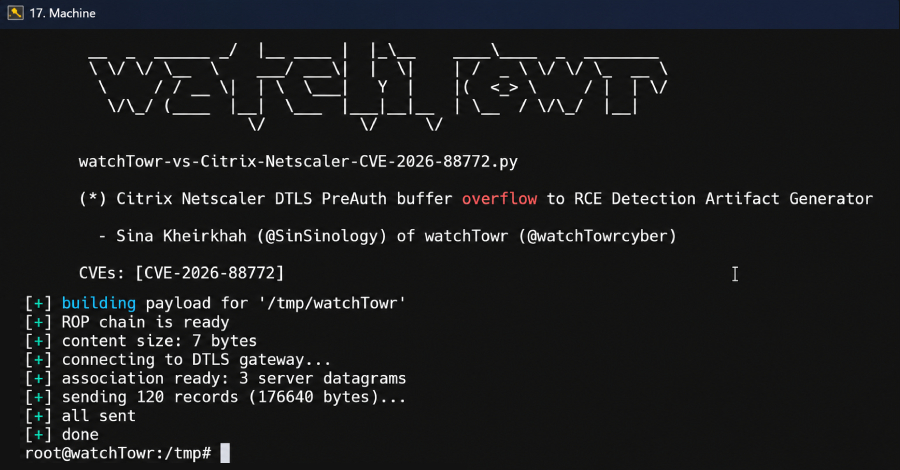
The development comes as three different flaws in NetScaler ADC and NetScaler Gateway appliances (CVE 2026-88771, CVE 2026-88772, and CVE 2026-88779) have come under active exploitation in the wild.
Found this article interesting? Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.