Ravie LakshmananJul 28, 2026Vulnerability / Threat Intelligence A maximum-severity security flaw impacting on-premises versions of Arista VeloCloud Orchestrator (VCO) has […]
Category: Attackers
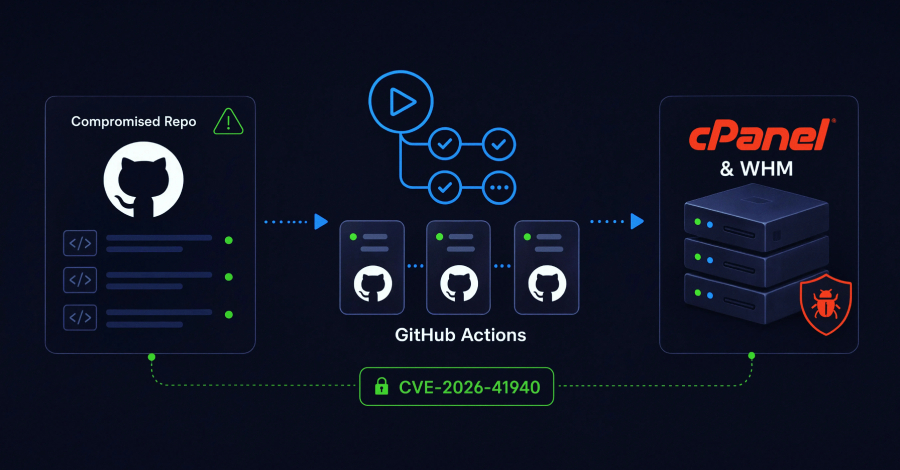
Attackers Weaponize GitHub Actions Runners to Target cPanel and WHM Servers
Cybersecurity researchers have shed light on a large-scale campaign that has turned compromised GitHub repositories into distributed attack infrastructure designed […]
Attackers Exploit ‘Ill Bloom’ Vulnerability to Drain $3.1 Million From Cryptocurrency Wallets
Security firm Coinspect has disclosed a crypto wallet flaw it calls Ill Bloom, and attackers are already using it. The flaw is in […]
Attackers Exploit SimpleHelp CVE-2026-48558 to Deploy TaskWeaver and Djinn Stealer
An unknown threat actor has been observed exploiting a recently disclosed maximum-severity security flaw in SimpleHelp to deliver two previously […]
Attackers Exploit Three Fortinet FortiSandbox Flaws, One Patched Last Week
Ravie LakshmananJun 16, 2026Vulnerability / Threat Intelligence Bad actors are exploiting multiple security vulnerabilities in Fortinet FortiSandbox, according to threat […]
Attackers Use LLM Agent for Post-Exploitation After Marimo CVE-2026-39987 Exploit
Ravie LakshmananMay 29, 2026Vulnerability / Artificial Intelligence An unknown threat actor has been observed using a large language model (LLM) […]
The Back Door Attackers Know About — and Most Security Teams Still Haven’t Closed
Every AI tool, workflow automation, and productivity app your employees connected to Google or Microsoft this year left something behind: […]
Attackers Don’t Just Send Phishing Emails. They Weaponize Your SOC’s Workload
The most dangerous phishing campaigns aren’t just designed to fool employees. Many are designed to exhaust the analysts investigating them. […]